Coming soon
QakBot: Email Thread Hijack to Cobalt Strike
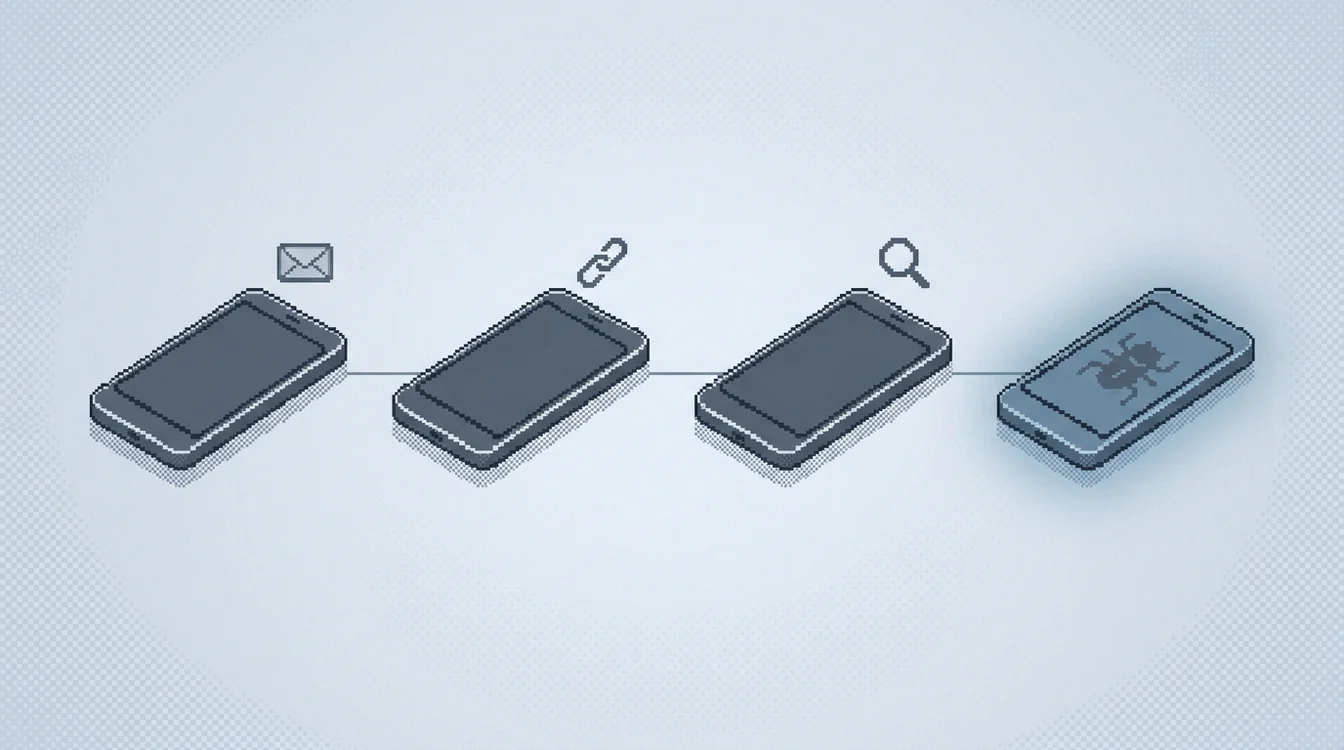
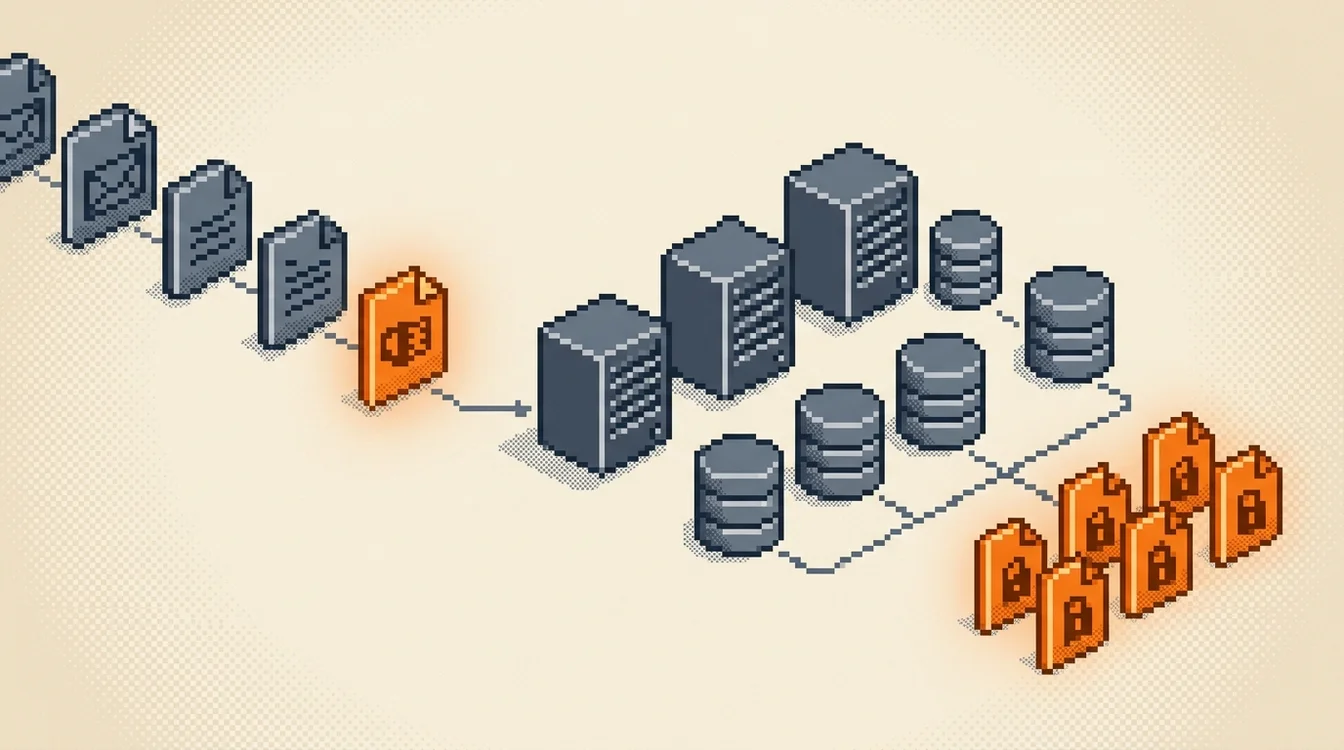
A freight coordinator received what looked like a reply from a trusted supplier. Hidden inside the ZIP attachment was a JavaScript dropper that fetched a QakBot DLL, registered it via regsvr32, and injected it into a system process. Minutes later a Cobalt Strike beacon followed, and the operator pivoted to the file server via WMI. Trace the kill chain from the spoofed email thread to lateral movement.
55m·50
Launches tomorrow (Nov 3)